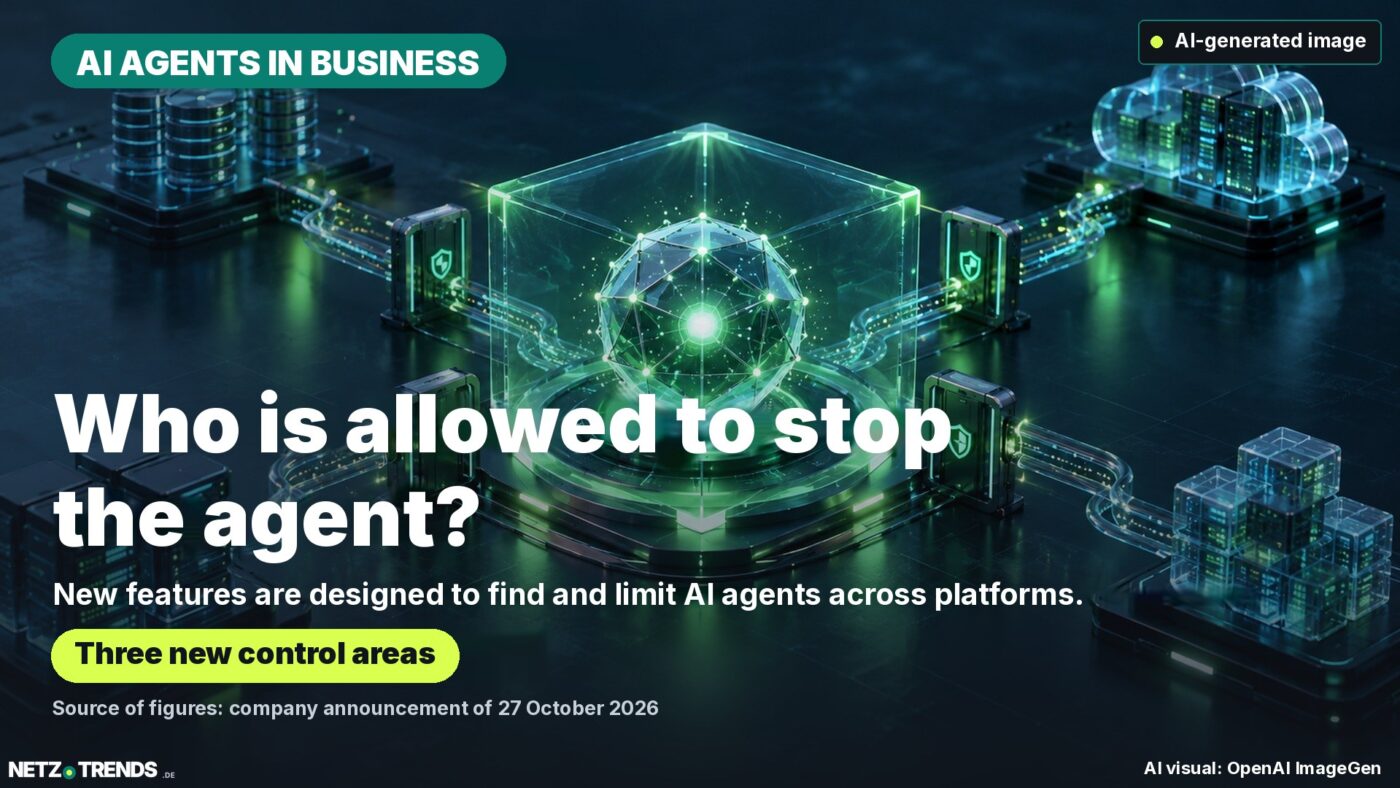
IBM is extending watsonx Orchestrate with features designed to find, isolate and evaluate AI agents across multiple platforms. Vault is set to limit their access as well.
Key points
- IBM is announcing new features for managing AI agents across different platforms.
- According to IBM, “Discover” and “Contain” will initially be available as a tech preview.
- “Evaluate” is meant to check quality, accuracy and compliance and to make model and token costs visible.
Companies are increasingly using AI agents for tasks in which software retrieves data, uses tools and runs workflows. IBM now wants to let organisations find and control such agents even when they were built outside its own platform. The announced watsonx Orchestrate features range from a central overview to isolating agents that behave suspiciously.
IBM presented the new features on 27 October 2026 at its TechXchange event. They focus on three areas: discovering agents, limiting their runtime behaviour and evaluating results. IBM describes discovery and containment as a tech preview; the announcement gives no date for general availability. Source: IBM Newsroom, 27 October 2026
What Orchestrate is set to do
With “Discover”, watsonx Orchestrate is meant to find agents created in third-party environments. IBM names Amazon Bedrock, Microsoft Foundry and Google Gemini. The feature is also meant to record models and MCP servers (Model Context Protocol servers that connect AI models to tools and data). The aim is to make agents visible without having to enter each one into a directory by hand. IBM explicitly lists this discovery feature as a tech preview, too.
“Contain” is designed to run agents in isolated environments so that a faulty or compromised agent cannot easily affect other agents. IBM also mentions a central kill switch that teams can use to stop an agent. According to IBM, this offering is also initially a tech preview. The announcement gives neither a specific date for general availability nor prices.
The third area is called “Evaluate”. IBM uses it to describe tests of quality, accuracy and compliance before deployment as well as monitoring during operation. A cost overview is meant to show which models an agent uses and how many tokens it consumes. The announcement does not describe this evaluation feature as a tech preview; however, no specific availability or contractual scope can be inferred from that.
Limiting identity and credentials
The Orchestrate features are part of a broader control approach. IBM describes Agent Identity as a registry recording who owns an agent, which lifecycle stage it is in and which permissions it has been granted. Together with HashiCorp Vault, short-lived credentials and permissions are to be used according to the principle of least privilege. According to IBM, access can be denied and a session terminated if an agent attempts an unapproved action.
This sets the announcement apart from a separate IBM post of 26 October, in which IBM announced the general availability of Agent Identity. The following day’s announcement focuses on the additional Orchestrate features for cross-platform discovery, containment and evaluation. IBM announcement on the general availability of Agent Identity
The integration with Vault is also meant to reduce reliance on long-lived secrets. According to IBM, Vault can provide task-specific, short-lived credentials; Vault 2.2 is set to give agents their own protected accounts and renew credentials automatically. These features do not replace careful permission management: they only work within the connected systems and the policies that have been set up.
What companies should consider
For companies that spread agents across several cloud and development environments, a central overview can help document responsibilities and access paths more clearly. This is an assessment based on the functionality IBM describes, not independent proof of effectiveness. The announcement contains no comparative test results and names no German customers or specific savings.
Before deploying in production, IT and security teams should therefore check which platforms are actually connected, which actions an agent may perform and how misbehaviour can be stopped. For “Discover” and “Contain”, they should also bear in mind that IBM initially labels them as a tech preview. A preview is no evidence that the features are already generally available for business-critical processes.
The product page describes IBM Agent Identity as a solution for registering, authenticating, authorising and managing agents across their lifecycle. It also lists delegation, runtime controls and audit logs as building blocks. IBM Agent Identity: product description
Frequently asked questions
Which new AI agent features is IBM presenting?
For watsonx Orchestrate, IBM is announcing the areas “Discover”, “Contain” and “Evaluate”. They are meant to let organisations find agents on several platforms, run them in isolation and evaluate them before and during operation.
Are “Discover” and “Contain” already generally available?
No. In its announcement of 27 October 2026, IBM describes both features as a tech preview. No date for general availability is given.
What role does HashiCorp Vault play?
Vault is meant to provide agents with short-lived, task-specific credentials. IBM also describes a link with Agent Identity so that permissions can be limited and revoked when unapproved actions occur.
Which controls for AI agents would matter most in your company – a complete overview, tight access rights or an immediate way to shut agents down? Feel free to share your view in the comments.
Sources and status
- IBM Newsroom: new identity and control features for AI agents, 27 October 2026
- IBM: Agent Identity is generally available, 26 October 2026
- IBM Agent Identity – product description
Research and data as of: 31 October 2026.
Transparency: This article is a translation of the German original on NETZ-TRENDS.de. It was researched and written with the support of artificial intelligence and is intended for human editorial review.